AI Usage Security
Keep secrets
out of the prompt.
Classic DLP can't read prompts. Anzenna reasons about them.
Source code, customer records, and strategy docs are being pasted into AI tools every day. Anzenna sees sensitive data leaving for generative tools and acts on intent, not just patterns.
The leak moved to the prompt.
When an employee pastes a customer list or a code repo into a personal AI account, the data moves as ordinary encrypted browser traffic. Classic DLP rules were never built to inspect it, so the most common modern leak is also the most invisible one.
Pattern matching is not enough. A regex for a credit card number cannot tell that a prompt is quietly exfiltrating strategy. The risk is in the behavior and the data context, not the string.
AI DLP has to understand who is sending what, to which tool, and whether that is normal for them, the way an analyst would.
The prompt left the browser.
Claude Desktop sends prompts straight from the laptop, where no browser extension can see them. Anzenna checks them against your DLP policy before they go, and a blocked prompt never reaches Claude.
Can you help me draft replies to today's open enrollment tickets?
Sure. Paste today's tickets and I'll draft a reply to each one.
Here are today's open enrollment tickets:J. Ames, SSN 123-45-6789, dental plan not showingK. Osei, SSN 078-05-1120, dependent not added
Anzenna DLP policy blocked this prompt (policy: SSNs in AI prompts).
Illustrative replay on sample data. The block text comes from the endpoint agent and arrives in place of Claude's reply.
The leak, handed to an agent.
Coding agents can send a file anywhere an MCP server reaches. Anzenna checks each MCP tool call against your DLP policy before it runs.
Illustrative replay on sample data. The block reason comes from the endpoint agent; Claude writes its reply.
The leak, traced back to a person.
Source code into ChatGPT. Financials into Claude. Customer records into an AI extension. Anzenna captures these flows and ties each one back to employee identity, behavioral history, and surrounding context, so you see exactly what is entering AI, through which path, and when it crosses the line.
- Browser uploads and MCP activity captured as they happen, not after the fact.
- Each flow scored against the person's role, baseline, and the data's sensitivity.
- Reads metadata over APIs, and the AI Usage console records who sent a prompt and which policy fired without displaying the prompt.
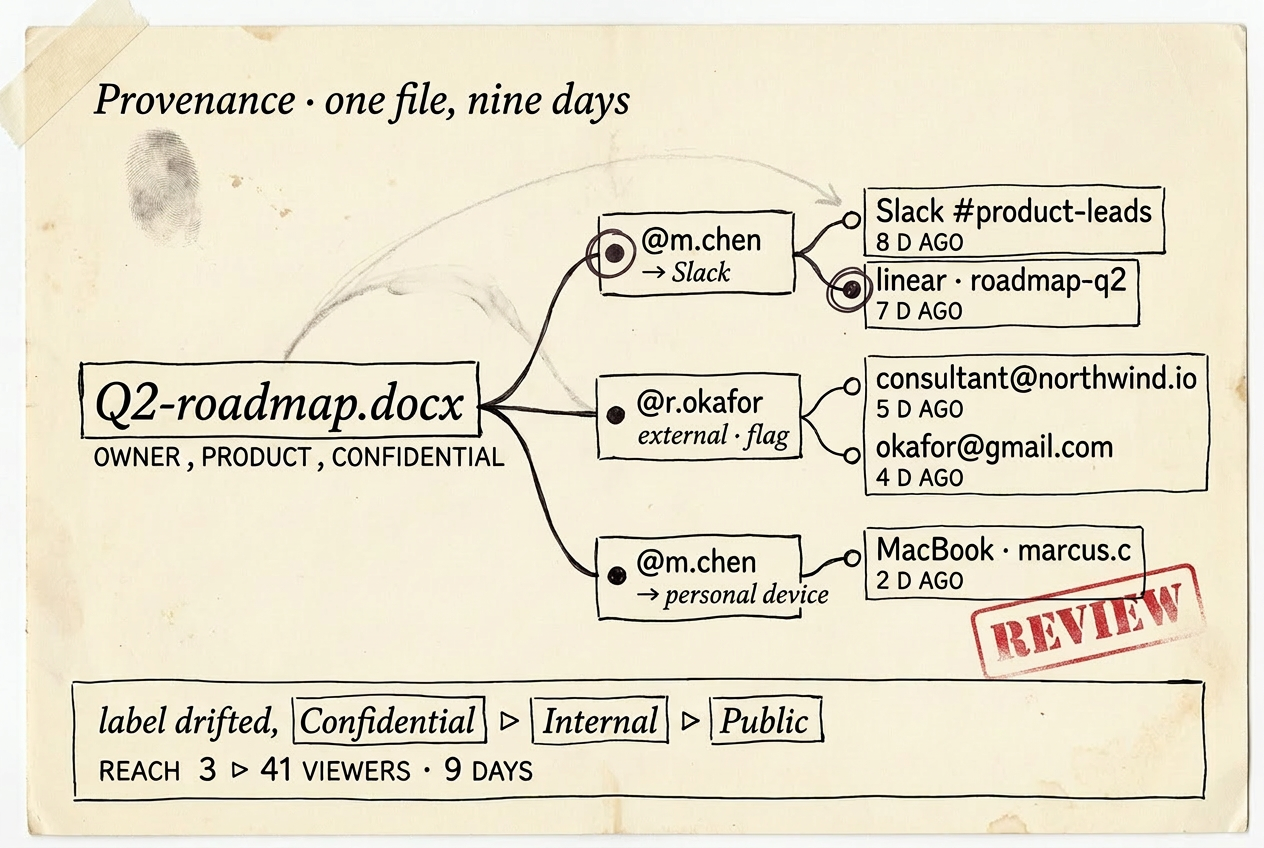
Same paste, different intent.
A prompt with sensitive data means nothing until you know who, and why.
A support agent summarizing a non-sensitive ticket in a sanctioned assistant.
A rushed employee pasting a customer list into a personal account to move faster.
A departing engineer feeding the core repo into an AI tool before the last day.
Protect data at the AI boundary.
Anzenna brings behavioral context to the moment sensitive data meets a generative tool or an AI agent.
See the data flows
Correlate identity, SaaS, and data signals to see where sensitive content is heading toward AI tools, sanctioned or shadow.
Weigh intent & context
Score each flow against a behavioral baseline, the person's role, and the sensitivity of the data, not a static rule.
Surface the real risk
Turn the noise into a prioritized, fully-reasoned case file: who, what data, which tool, and why it matters.
Remediate
Block, quarantine, revoke access, or notify, with a transparent audit trail and one-click action.
Rules match strings. Anzenna reads behavior.
Traditional DLP inspects content against patterns on channels it can decrypt. Anzenna reasons over behavior, identity, and data context, so leaks into AI tools surface even when they ride ordinary encrypted traffic.
| Capability | Anzenna | Traditional DLP |
|---|---|---|
| Covers prompts & generative tools | Yes | No |
| Catches data sent to personal AI accounts | Yes | No |
| Checks AI agent tool calls before they run | Yes | No |
| Understands intent & behavior | Yes | No |
| Output | A verdict and a reasoned case file | Blocked event or raw alert |
| False positives | 90% fewer alerts to analysts | About half of alerts are false |
| Deployment | Live in minutes over APIs, with an endpoint agent where AI coding tools or Claude Desktop run | Proxies & endpoint agents |
AI DLP, at a glance.
- Prevents sensitive data leaking into AI tools, including prompts and personal accounts that classic DLP never inspects.
- Acts on intent and behavior, not just patterns, in the browser, and checks prompts in Claude Desktop and MCP tool calls in Claude Code before they go out.
- Surfaces risky flows as reasoned cases with one-click action.
Your stack, unchanged.
Fifteen-minute install. Read-only by default. An endpoint agent only where AI coding tools or Claude Desktop run.


Common questions.
Can Anzenna stop data going into ChatGPT or Claude?
Yes. Anzenna correlates identity, SaaS, and data signals to surface sensitive content heading toward generative tools, including personal accounts, and can revoke access or notify in one click. It reasons over behavior, so it catches flows that classic DLP rules miss.
Can Anzenna stop an AI agent from moving sensitive files?
Yes, for coding agents such as Claude Code. Anzenna's endpoint agent checks each MCP tool call before it runs, so a create_file call carrying customer data to a personal Dropbox can be blocked by a DLP policy from the same builder you use for the browser, set to the MCP tool call channel. Each attempt the endpoint agent sees is recorded and can feed an investigation.
Does Anzenna cover prompts sent from Claude Desktop?
Yes. Anzenna's endpoint agent checks prompts sent from Claude Desktop against your DLP policy before they are forwarded, so a blocked prompt never reaches Claude. The attempt is recorded in the console with the person and the verdict attached.
Does it replace our existing DLP?
Either. Anzenna can consolidate DLP and UEBA, or integrate with your existing DLP to inherit its classifications while adding the behavioral context and AI coverage rule-based DLP lacks.
How does it avoid drowning us in alerts?
Instead of firing on every pattern match, Anzenna scores each flow against behavior and data context, then assembles a prioritized case file. In production that means roughly 90% fewer alerts surface to analysts.
Does Anzenna read the content of prompts?
Yes, where a DLP policy covers AI prompts. Anzenna checks the prompt against that policy before it is sent, and for Claude Desktop the console records the person and the policy that fired without displaying the prompt. Outside DLP checks, Anzenna works from metadata and behavioral signals, with read-only access that is revocable at any time. It is SOC 2 Type II compliant and Microsoft 365 security certified.
Govern AI end to end.
All five AI controls in one picture: see the AI usage control overview →