AI DLP and insider risk,
on one Identity-Data-Action graph
Anzenna reads 130+ identity, SaaS, cloud and security sources and adds a browser extension and endpoint agent where data leaves. It ties every AI action and data movement to the person behind it and hands your team a finished case instead of an alert.
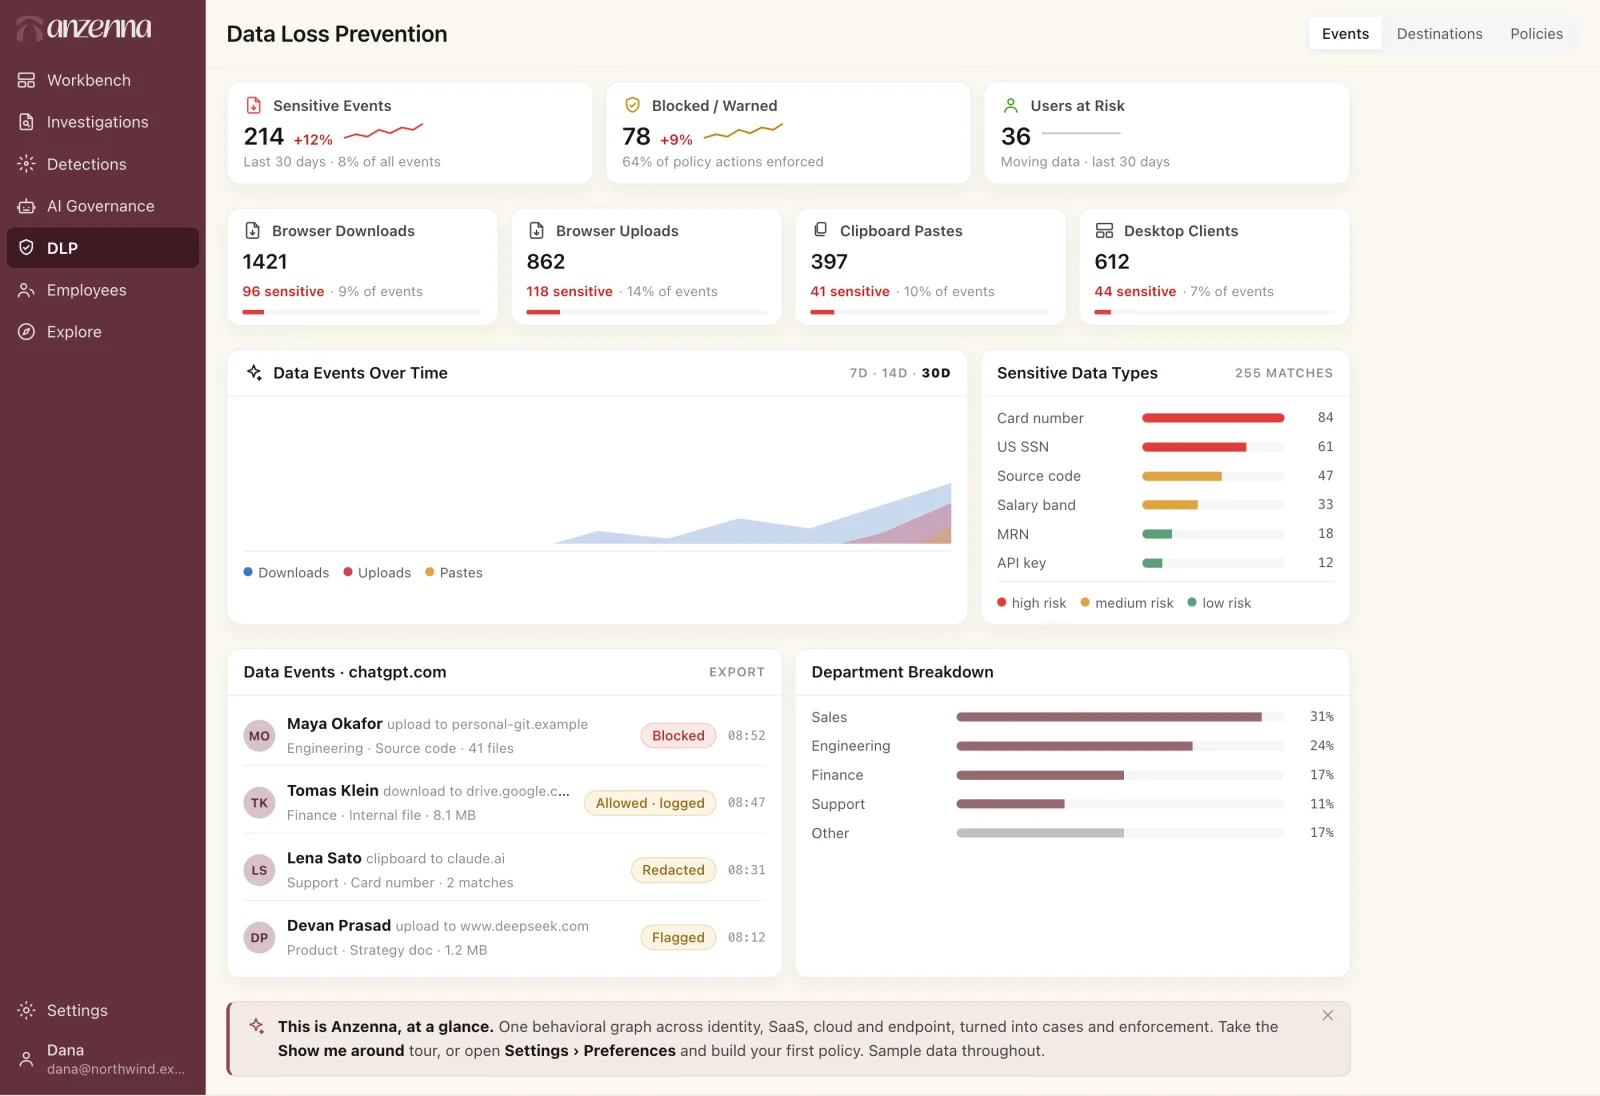
Drive the console yourself
An interactive tour of the Anzenna console. On the AI DLP side, write a data-protection policy in plain language and watch the verdict land on the employee's screen. Flip to Insider Risk to open a live investigation, follow the evidence timeline, and read the agent's reasoning. Sample data throughout.
The sensing layer
Lightweight integrations across 130+ sources, plus a browser extension and endpoint agent at the AI boundary. Okta, Google Workspace, Microsoft 365, GitHub, Slack, Snowflake, and more. Rolls out through your MDM.
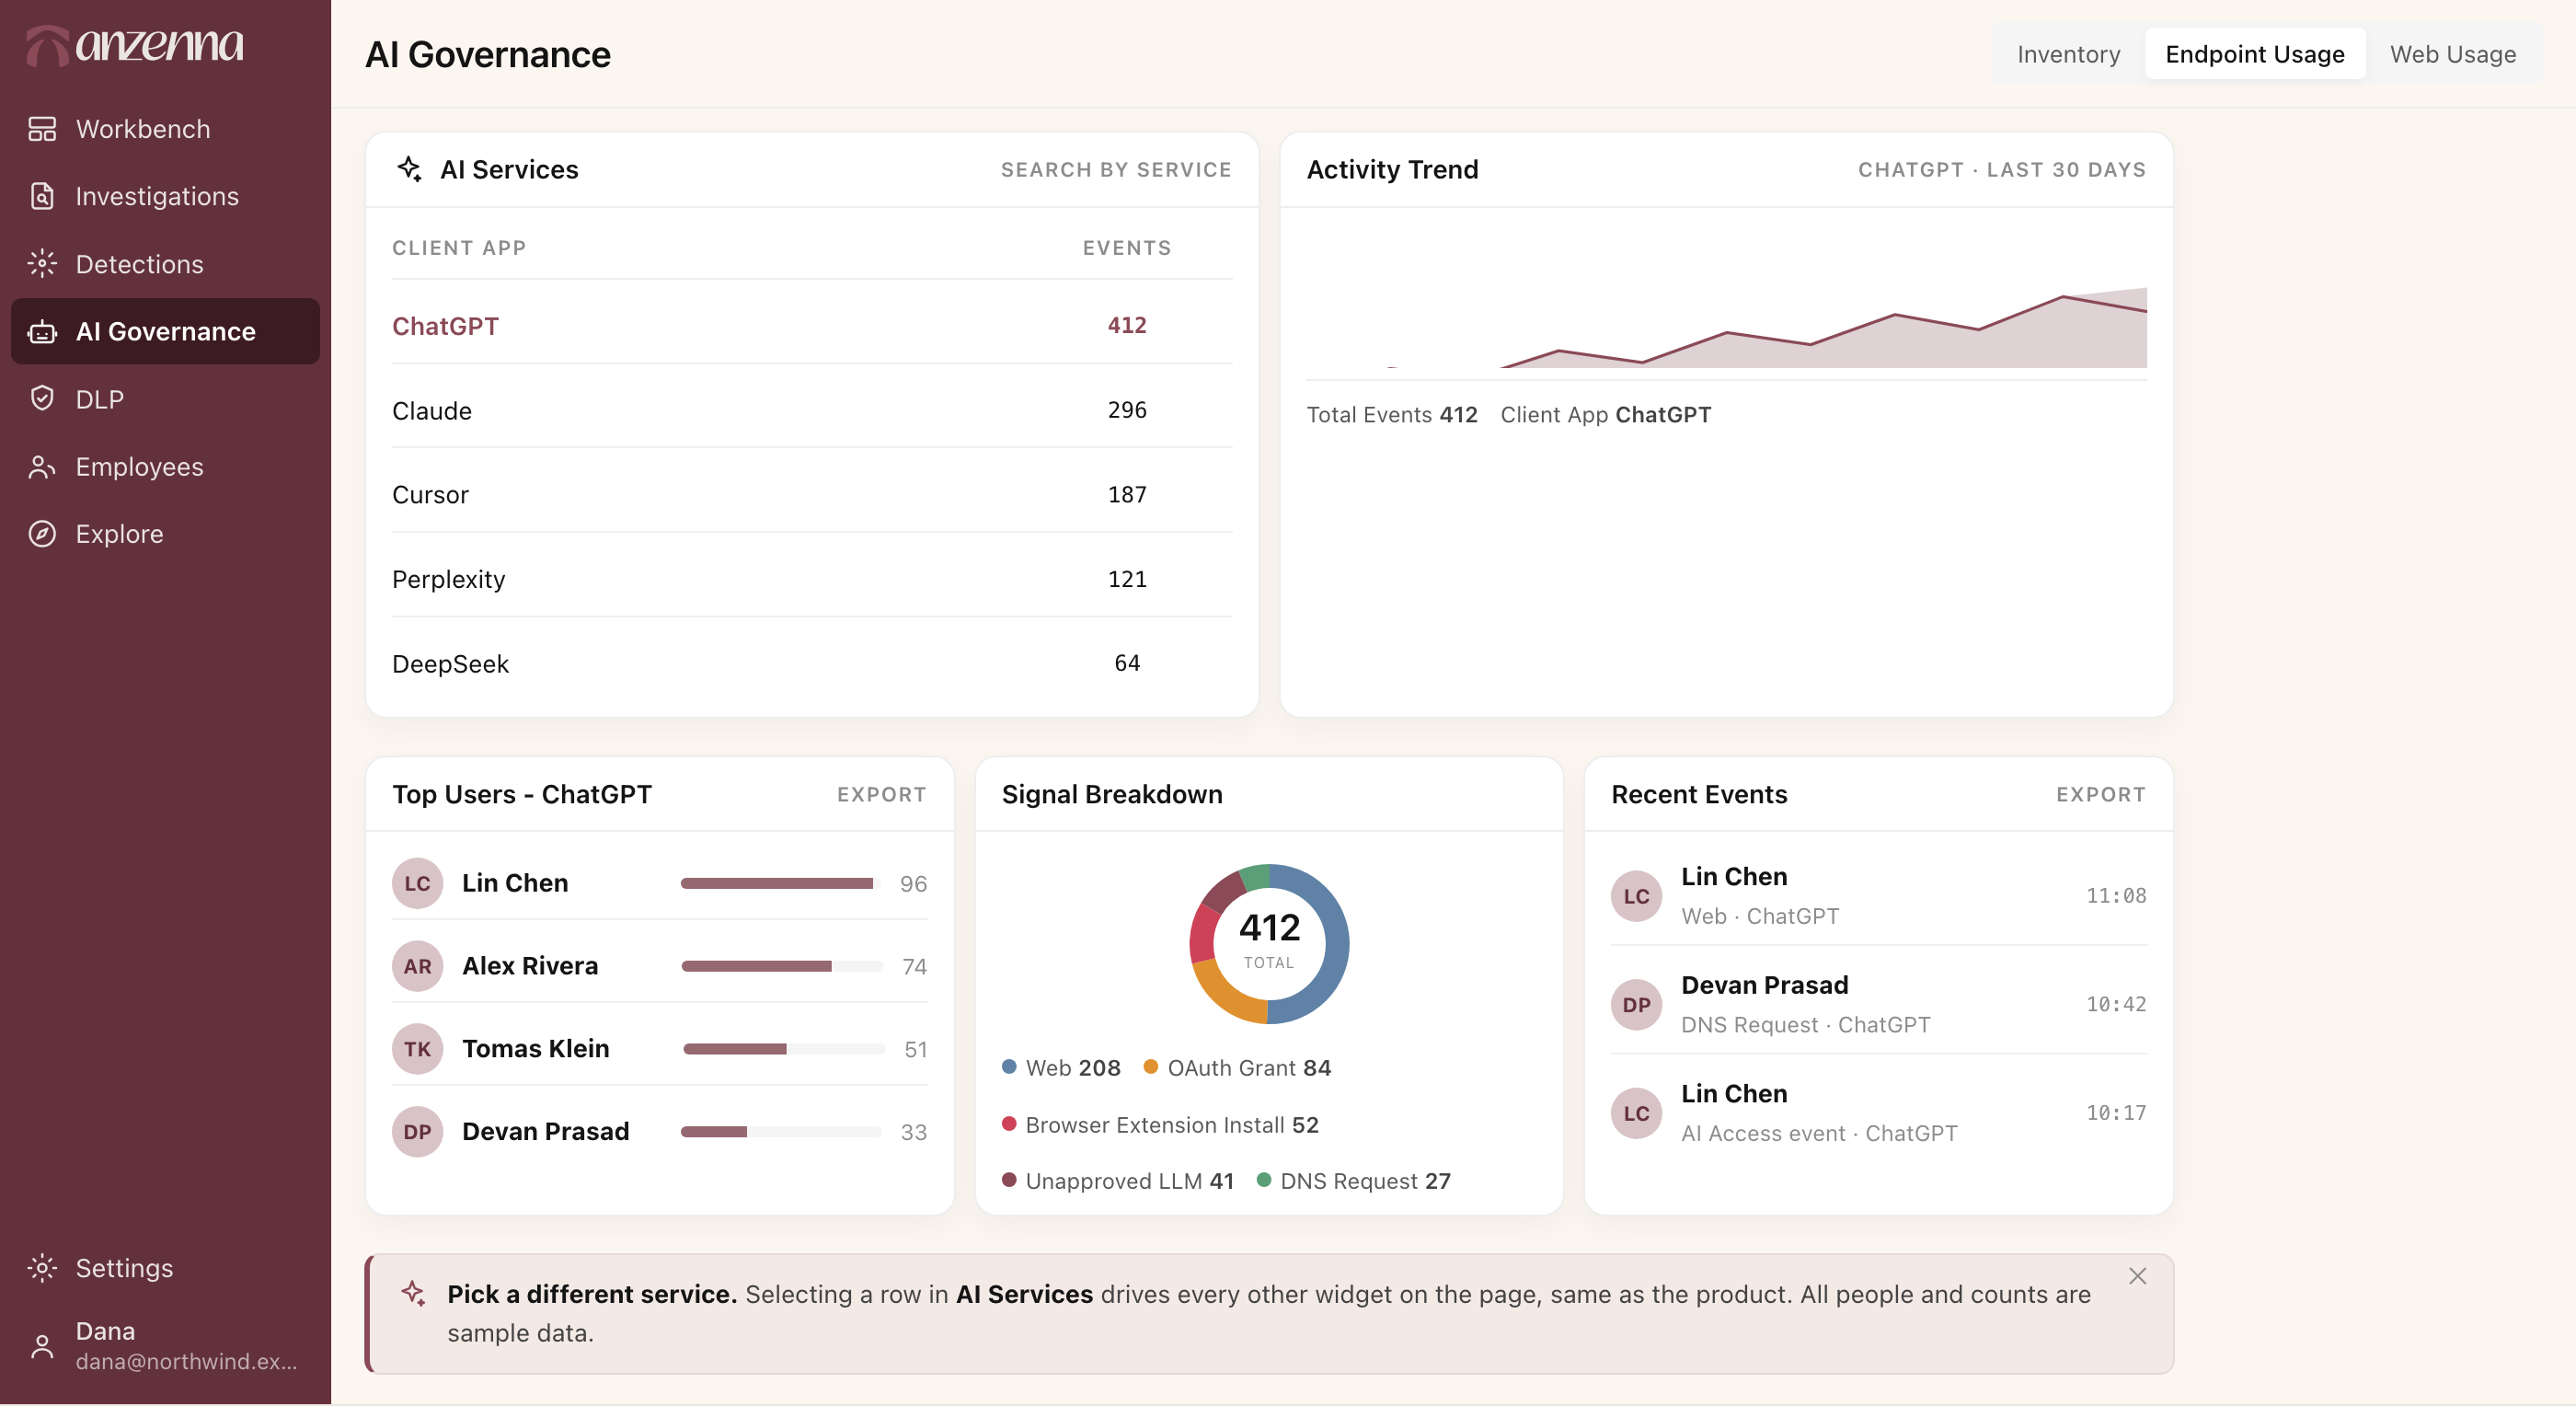
The reasoning layer
The Identity-Data-Action graph links people, data and AI use. Investigation agents tie every AI action and data movement to a person and weigh it against their peer-group baseline, catching what rule-based DLP and static thresholds miss.
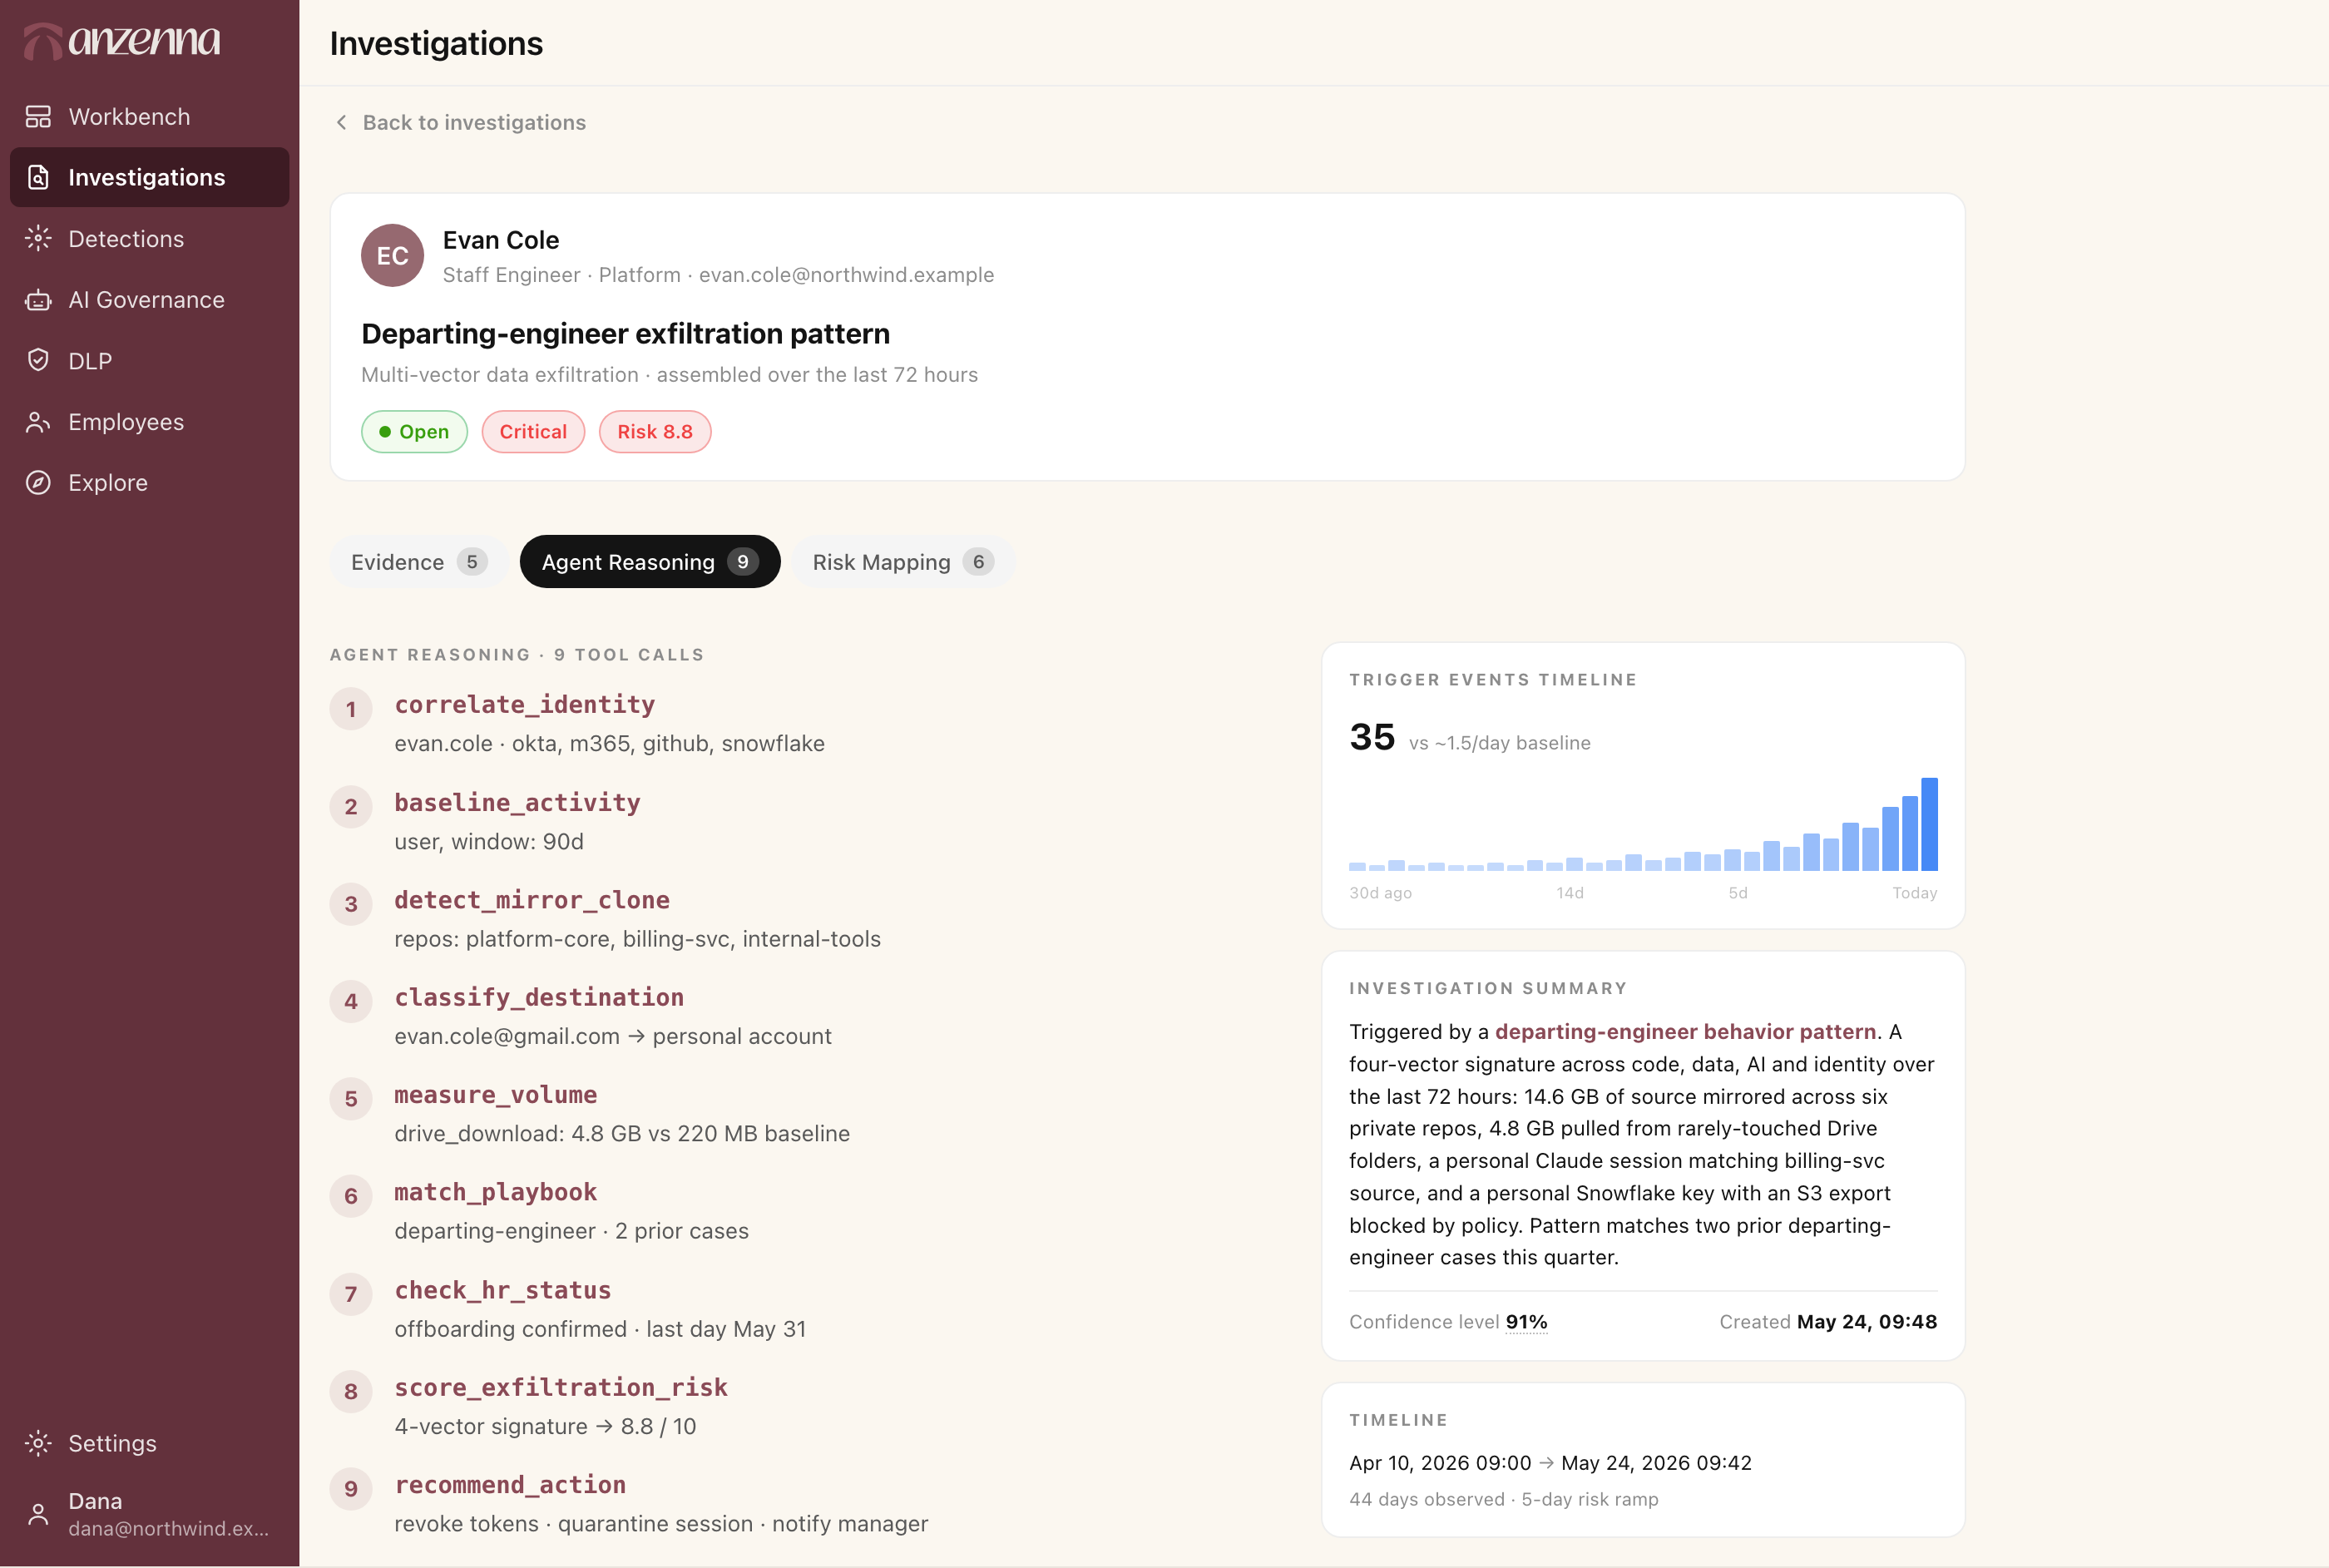
The action layer
One workspace for AI DLP and insider-risk teams. Case files written by an agent, reviewed by a human, audited end-to-end. Signal, not noise.
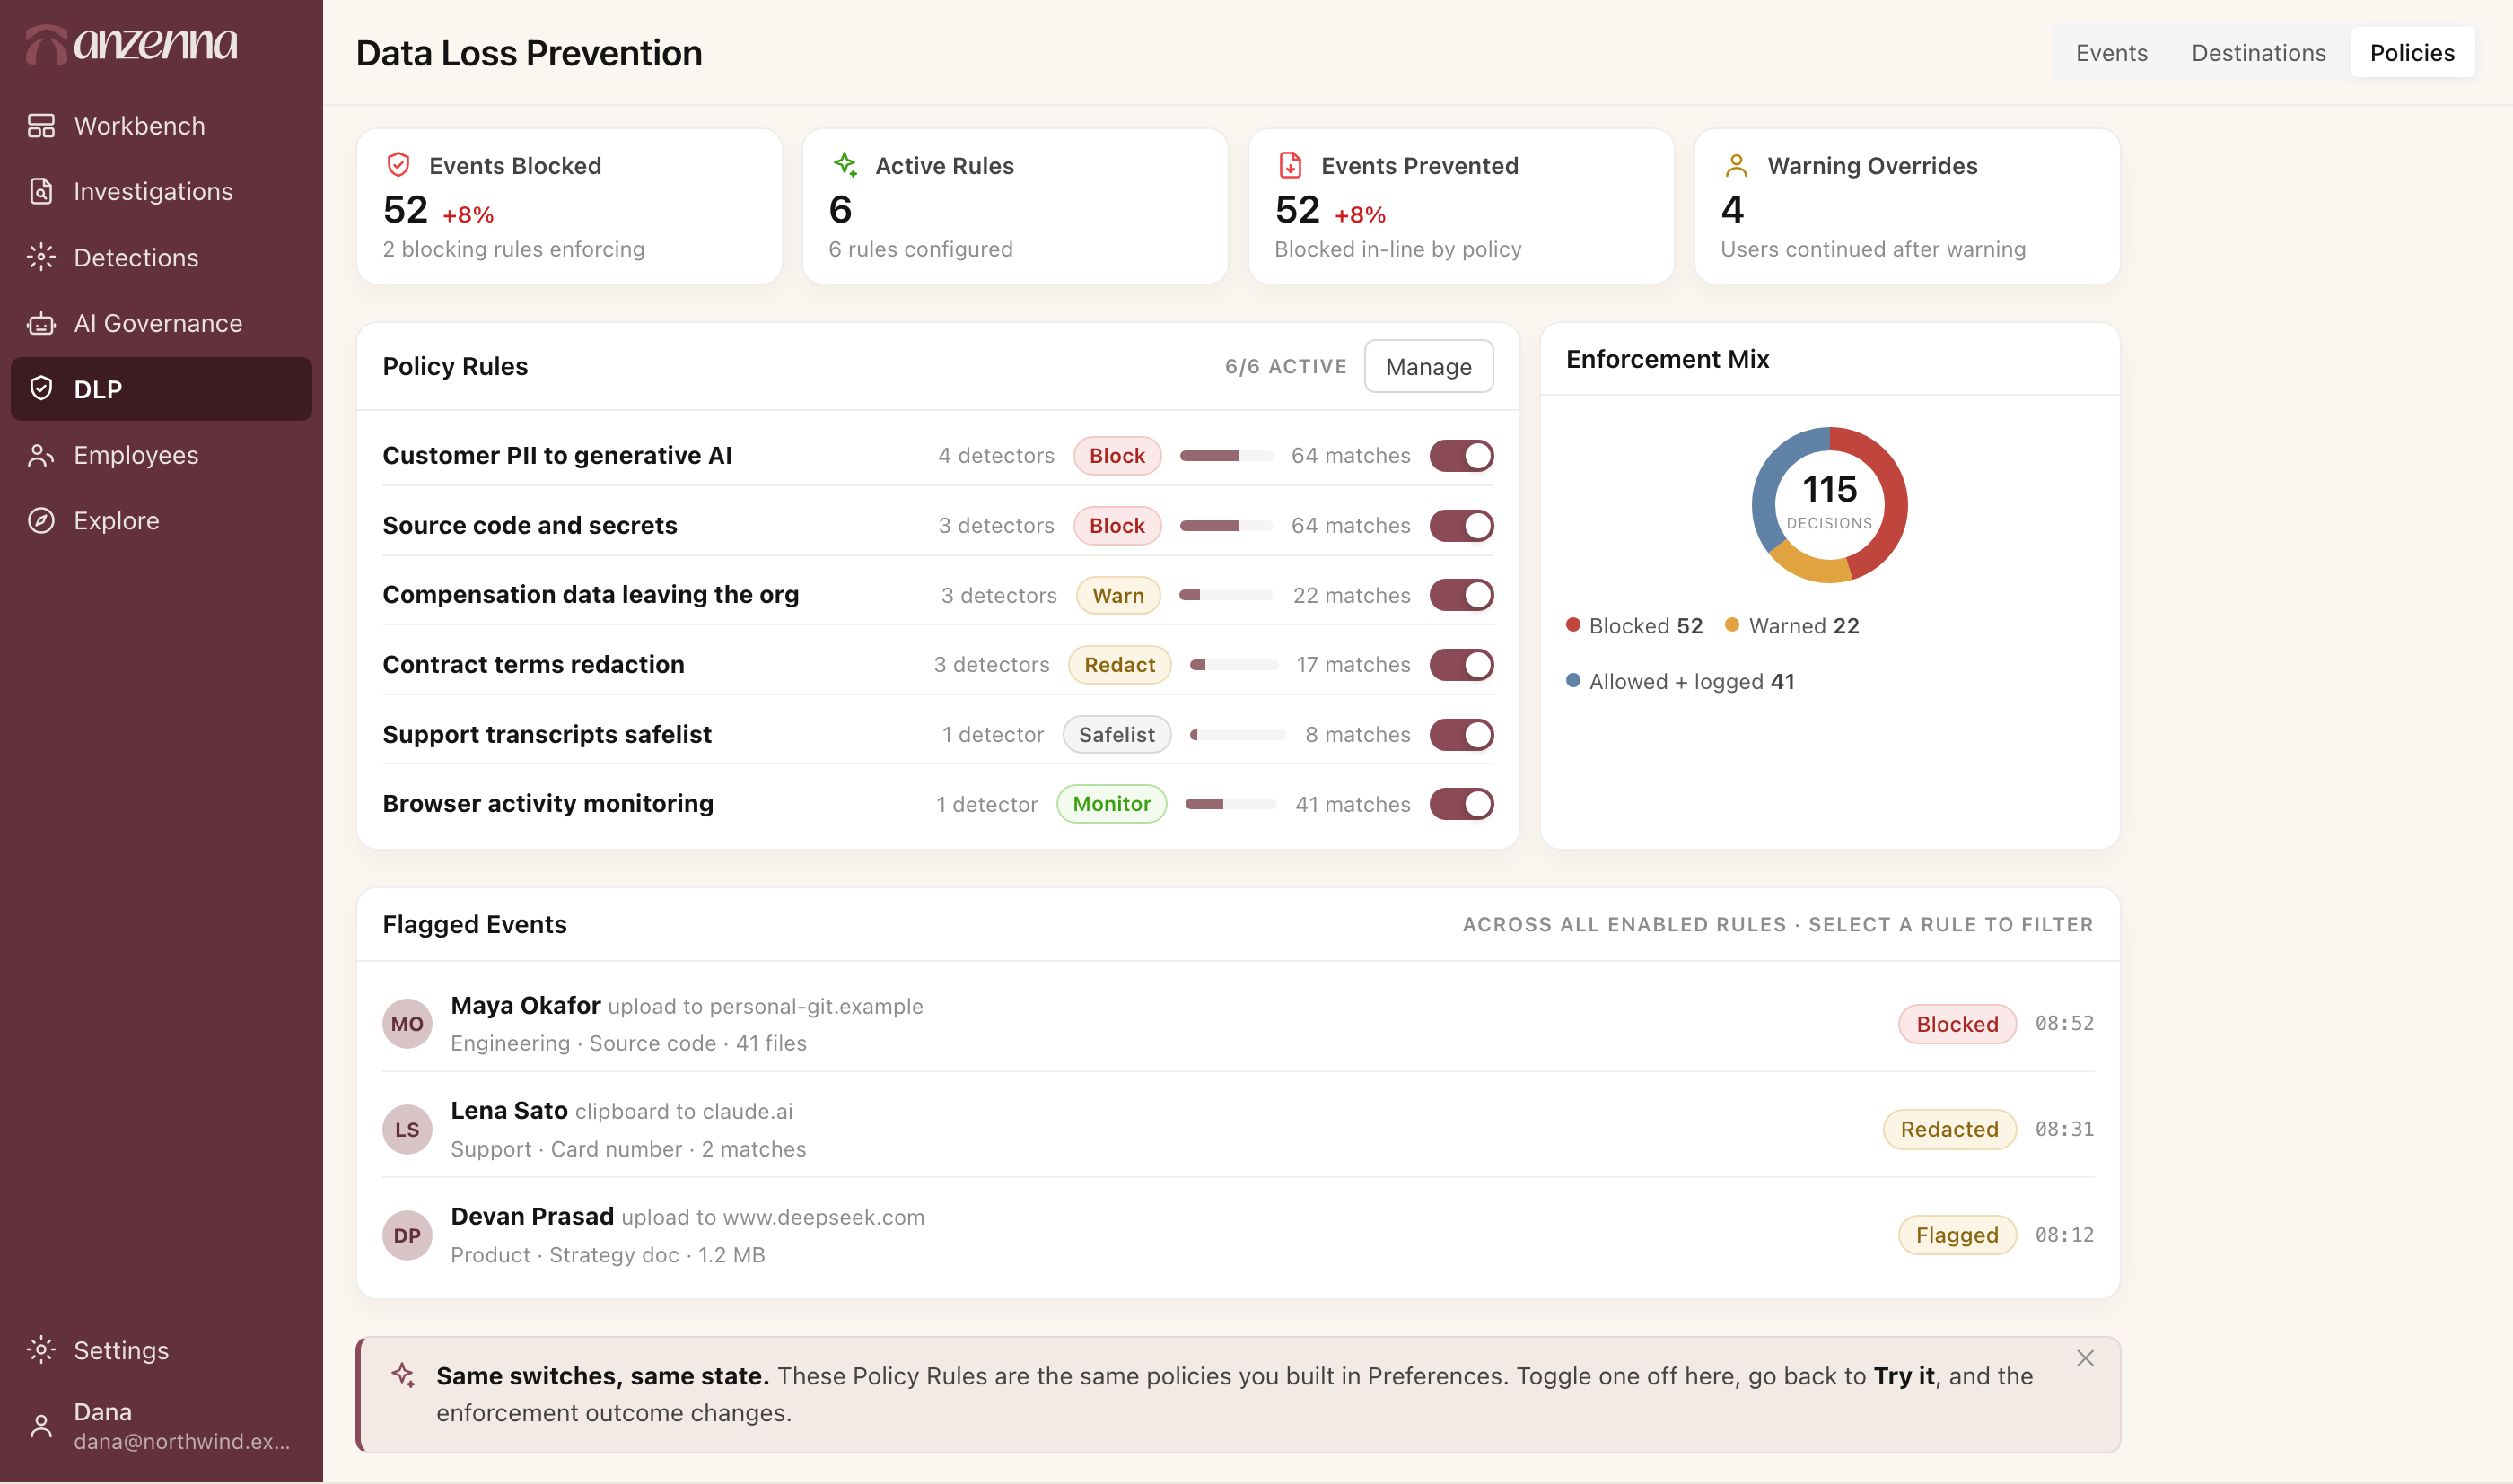
Built for the full picture
See the AI boundary.
Every AI tool your people reach, sanctioned or shadow, and every sensitive paste, upload, or prompt heading into it.
Weigh by behavior.
Peer-group baselines, not thresholds. Each person's AI use and data movement measured against their own past and their team's rhythm.
Act in one motion.
Block, redact, revoke, or quarantine at the moment of risk, with a case file and full audit trail behind every decision.
No alert fatigue.
The agent decides what matters and drops what doesn't. A queue of cases, not a wall of alerts.
Protect the human.
Evidence before action. A person reviews every consequential decision, so trust and due process are preserved.
One workflow.
Security, HR, and legal on the same insider case, with no gaps, no re-explaining, no lost context.
Ready to see it on your data?
The platform, in plain terms.
- Anzenna is AI DLP and insider risk management, on one Identity-Data-Action graph that spans identity, endpoint, browser, SaaS and cloud.
- It catches sensitive data heading for AI tools and the insider risk building behind it, then AI investigation agents turn the signals into a defensible case file, so your analysts decide instead of search.
- It reasons over behavior and context to separate real risk from noise across the whole stack, from one place.
- One platform for six jobs: AI DLP, insider risk, identity threats, data and IP protection, alert triage, and SaaS posture.
- See it on your own environment in a 30-minute demo.
Answered, plainly.
What is the Anzenna platform?
A platform for AI DLP and insider risk management. It unifies identity, endpoint, browser, SaaS, and cloud into one Identity-Data-Action graph and runs AI investigation agents on top, so you see and act on real risk from one place, without the alert fatigue.
How do the investigation agents work?
They correlate signals across your stack, gather the surrounding evidence, weigh it against a 90-day behavioral baseline, and produce a defensible case file with a recommended action, in under 2 minutes median.
What gets installed?
Most of Anzenna runs over API connections to your identity provider, SaaS, cloud and security tools, and those take minutes to set up. For AI DLP you add a browser extension for Chrome, Edge and Firefox, plus an endpoint agent on Mac and Windows where people use Claude Code, Cursor or desktop AI apps. Both roll out through the MDM you already use, such as Jamf, Intune or Kandji.
What does the platform connect to?
130+ sources, including Okta, Microsoft 365, Google Workspace, GitHub, Snowflake, CrowdStrike, Slack, and Salesforce. See the full list on the integrations page.
Does it replace my SIEM, DLP, or UEBA?
It sits on top of your SIEM and tools, adding the correlation and reasoning that turn raw alerts into investigations, and it can consolidate DLP (data loss prevention) and UEBA (user and entity behavior analytics).
Is Anzenna secure and compliant?
Anzenna is SOC 2 (System and Organization Controls) Type II attested and Microsoft 365 certified. API connections use read-only, revocable access wherever the tool allows.